Best Key Storage Solutions for Vagrant to Buy in September 2026
Uniclife 20-Key Steel Key Cabinet, Black Key Box with Combination Lock
- STORE UP TO 20 KEYS: OPTIMIZED FOR SPACE, IDEAL FOR ANY SETTING!
- SECURE 3-DIGIT COMBO: 1,000 LOCK OPTIONS FOR EXCLUSIVE ACCESS!
- COLOR-CODED TAGS: EASILY LABEL KEYS FOR QUICK IDENTIFICATION!
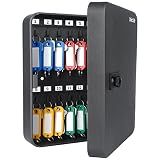
Uniclife 28-Key Steel Key Cabinet, Black Key Box with Combination Lock
-
MAXIMIZE STORAGE: HOLDS 28 KEYS FOR HOMES, SCHOOLS, AND OFFICES.
-
SECURE ACCESS: 3-DIGIT LOCK OFFERS 1,000 UNIQUE COMBINATIONS.
-
ORGANIZED SYSTEM: COLOR-CODED TAGS AND NUMBERED STICKERS FOR EASY TRACKING.
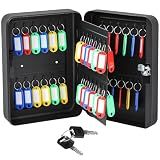
Ripeng 48-Keys Steel Key Lock Box - Wall Mount Key Cabinet with Colorful SecureTags & Hooks Keys Organizer Storage for Home Office Hotel Rental Business Property Management, Black
-
SPACIOUS 48-KEY CAPACITY: ORGANIZE KEYS FOR OFFICES & HOTELS.
-
COMPLETE ORGANIZATION: COLORFUL TAGS ENSURE EASY KEY IDENTIFICATION.
-
DURABLE ALLOY STEEL: LONG-LASTING SECURITY FOR BUSY ENVIRONMENTS.
Amazon Basics Locking Steel Security Cabinet Key Lock Box with 48 Key Hooks, Key Storage, 2.8"D x 7"W x 9.8"H, Black
- SECURELY STORE UP TO 48 KEYS; PERFECT FOR HOMES OR OFFICES.
- DURABLE STEEL CONSTRUCTION WITH A SLEEK BLACK FINISH.
- INCLUDES TAGS AND MOUNTING HARDWARE FOR EASY SETUP.
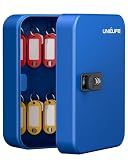
Uniclife 20 Position Key Cabinet with Combination Lock Resettable Blue Digital Security Storage Box Steel Key Organizer with Colorful Key Tag Labels Stickers and Hooks
-
MAXIMIZE SPACE: HOLDS UP TO 20 KEYS, PERFECT FOR ANY SETTING!
-
SECURE ACCESS: 3-DIGIT COMBINATION LOCK OFFERS 1,000 UNIQUE CODES.
-
EASY ORGANIZATION: INCLUDES TAGS, STICKERS, AND HOOKS FOR NEAT TRACKING.
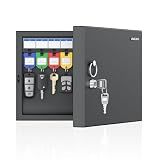
Uniclife 16 Keys Key Lock Box, Wall Mount Key Box, Car Key Organizer with Writable Key Racks and Tags, Security Key Cabinet, Car Key Holder Storage Box for Office, Hotel & Company
- SPACIOUS 16-KEY DESIGN: ORGANIZES DOZENS OF KEYS EFFORTLESSLY.
- ENHANCED SECURITY FEATURES: HEAVY-DUTY STEEL PREVENTS UNAUTHORIZED ACCESS.
- QUICK KEY IDENTIFICATION: COLOR-CODED TAGS ENSURE INSTANT VISIBILITY.
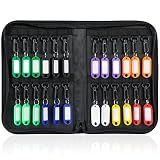
Uniclife 24-Hook Portable Key Organizer, Zippered Key Case for Offices
-
PORTABLE DESIGN: COMPACT SIZE HOLDS 24 KEYS, PERFECT FOR ON-THE-GO CONVENIENCE.
-
WATERTIGHT & FIREPROOF: RESISTS EXTREME TEMPS UP TO 2000°F, KEEPS KEYS SAFE.
-
FLEXIBLE HOOKS & TAGS: EASY ORGANIZATION WITH ROTATING HOOKS AND COLORFUL LABELS.
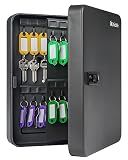
Uniclife 60 Position Key Cabinet with Combination Lock Resettable Black Digital Security Storage Box Steel Key Organizer with Colorful Key Tag Labels Stickers and Hooks
-
SPACIOUS 2-LAYER DESIGN HOLDS 60 KEYS-PERFECT FOR ANY SETTING!
-
SECURE 3-DIGIT COMBINATION LOCK ENSURES EXCLUSIVE KEY ACCESS.
-
COLORFUL TAGS AND STICKERS MAKE KEY TRACKING QUICK AND EASY!
When working with Vagrant and storing API keys, it is important to keep them secure and separate from your project files. One common practice is to store API keys in environment variables. You can create a .env file in your project directory and store your keys there, then load them into your Vagrantfile or provisioning script using a tool like dotenv to keep them secure. Another option is to use a key management service like AWS Secrets Manager to securely store and retrieve your keys during provisioning. Remember to never hardcode API keys directly into your Vagrantfile or any source code, as this can pose a security risk.
What is the best practice for storing API keys in Vagrant?
The best practice for storing API keys in Vagrant is to use environment variables. You can use environment variables to store sensitive information such as API keys securely without exposing them in your Vagrantfile or version control system.
To set environment variables in Vagrant, you can use the config.vm.provision block to set the variables when provisioning the virtual machine. For example, you can add the following lines to your Vagrantfile to set an API key as an environment variable:
Vagrant.configure("2") do |config| config.vm.provision "shell", inline: <<-SHELL export API_KEY=your_api_key_here SHELL end
You can then access the API key in your scripts or applications running in the virtual machine by reading the value of the environment variable API_KEY.
By using environment variables to store API keys in Vagrant, you can ensure that sensitive information is kept secure and not exposed in your codebase. Additionally, using environment variables makes it easy to manage and update API keys without having to modify your Vagrantfile.
What is the recommended way to store authentication tokens in Vagrant?
The recommended way to store authentication tokens in Vagrant is to use environment variables. This ensures that sensitive information such as passwords or authentication tokens are not hard-coded in your Vagrantfile or other configuration files, which could pose a security risk. By using environment variables, you can easily set and access these values without exposing them to potential risks. Additionally, you can use tools like dotenv to manage and load environment variables from a .env file.
What is the best way to automate API key storage in Vagrant?
One common and secure way to automate API key storage in Vagrant is by using environment variables. This involves storing the API key as an environment variable in the Vagrantfile or in a separate .env file, and then accessing the key in your Vagrant configuration or provisioning scripts.
Here are the steps to automate API key storage in Vagrant using environment variables:
- Store the API key in an environment variable: You can store the API key as an environment variable in the Vagrantfile or in a separate .env file. For example, in the Vagrantfile:
ENV['API_KEY'] = 'YOUR_API_KEY_HERE'
- Access the API key in your Vagrant configuration or provisioning scripts: In your Vagrant configuration or provisioning scripts, you can access the API key using the ENV global variable. For example:
api_key = ENV['API_KEY']
- Use the API key in your provisioning scripts or applications: You can now use the API key in your provisioning scripts or applications to authenticate with the API. For example, you can pass the API key to a command line tool or set it as an environment variable in your application.
By using environment variables to store and access API keys in Vagrant, you can keep the keys secure and easily automate their storage and usage in your development environment. Additionally, you can easily change or update the keys without modifying your configuration files.
How to restrict access to API keys in Vagrant?
To restrict access to API keys in Vagrant, consider implementing the following best practices:
- Store API keys securely: Avoid hardcoding API keys in your Vagrantfile or code. Instead, store them in a separate configuration file or use environment variables to keep them secure.
- Use a configuration management tool: Use tools like Ansible or Puppet to manage and deploy your API keys securely. These tools provide functionalities to store sensitive information securely and restrict access to authorized users.
- Encrypt sensitive data: Encrypt API keys and other sensitive information before storing them in configuration files or environment variables. This adds an extra layer of security and ensures that the keys are not exposed to unauthorized users.
- Use file permissions: Set strict file permissions for files containing API keys to restrict access to authorized users only. Limit read and write permissions to ensure that only trusted individuals can access or modify the keys.
- Monitor access and usage: Keep track of who has access to API keys and monitor their usage to detect any unauthorized access or suspicious activities. Implement logging and auditing mechanisms to record and analyze access patterns.
By following these practices, you can restrict access to API keys in Vagrant and ensure that sensitive information remains secure and protected from unauthorized access.